Managing TLS Certificates Using Ansible and Let’s Encrypt! PART 2:
This tutorial will guide you through using Ansible AWX/AAP to request a Let’s Encrypt certificate and securely storing your Cloudflare API key. This is the Second part of a series on managing SSL certificate lifecycles using Ansible, progressing from Ansible Core to advanced automation with AWX, Ansible Automation Platform, and integration with GitOps and ServiceNow.
part 2 of 6 · series Let's Encrypt with Ansible
- 1Request a certificate with Ansible Core
- 2Run it from AWX / AAP with GitOps
- 2.1Deploy to Cisco ASA
- 2.2Deploy to F5 BIG-IP
- 3Scheduled auto-renewal workflows
- 4ServiceNow change and catalog integration
collections/requirements.yml in one GitLab repository and create a second, empty cert-store repository for the issued certificates. In AWX/AAP you add two custom credential types (one for the Cloudflare API token, one for the cert-store GitLab login), a source control credential, a project, and a job template with a survey for fqdn and email. Launching the template requests the certificate and commits it to cert-store, so every certificate is stored and versioned in Git.Part 2: Managing Certificates with AWX/Ansible Automation Platform and GitOps
Introduction
Continuing from Part 1, this tutorial will guide you through managing Let’s Encrypt certificates using AWX/Ansible Automation Platform. We can use the exact same playbook from part 1 with a few modifications. You will also have to make sure you have a few Prerequisites setup a head of time.
Prerequisites
- AWX/Ansible Automation Platform installed and configured. In this part will be using the Ansible GUI version AWX/AAP
- GitLab - AWX/AAP both require that your playbooks are stored in a central git repository I will be using GitLab. You will need two repositories:
- The first repository will be for holding the playbook and other required files. You can copy or clone my repository
- The second will be a repository for storing your certificates.
- Credentials for AWX/Ansible Automation Platform and GitLab
- Cloudflare account with API token
- Basic knowledge of Git.
- LDAP or Active Directory logins? If your AAP users sign in through LDAP, read the AAP 2.5 lowercase DN gotcha before you map teams and roles.
What You Will Learn
- Configuration of AWX/Ansible Automation Platform projects
- Integrating AWX with GitLab
- Running Playbooks and Automating Certificate Requests
Gitlab setup
1. Setup Repositories
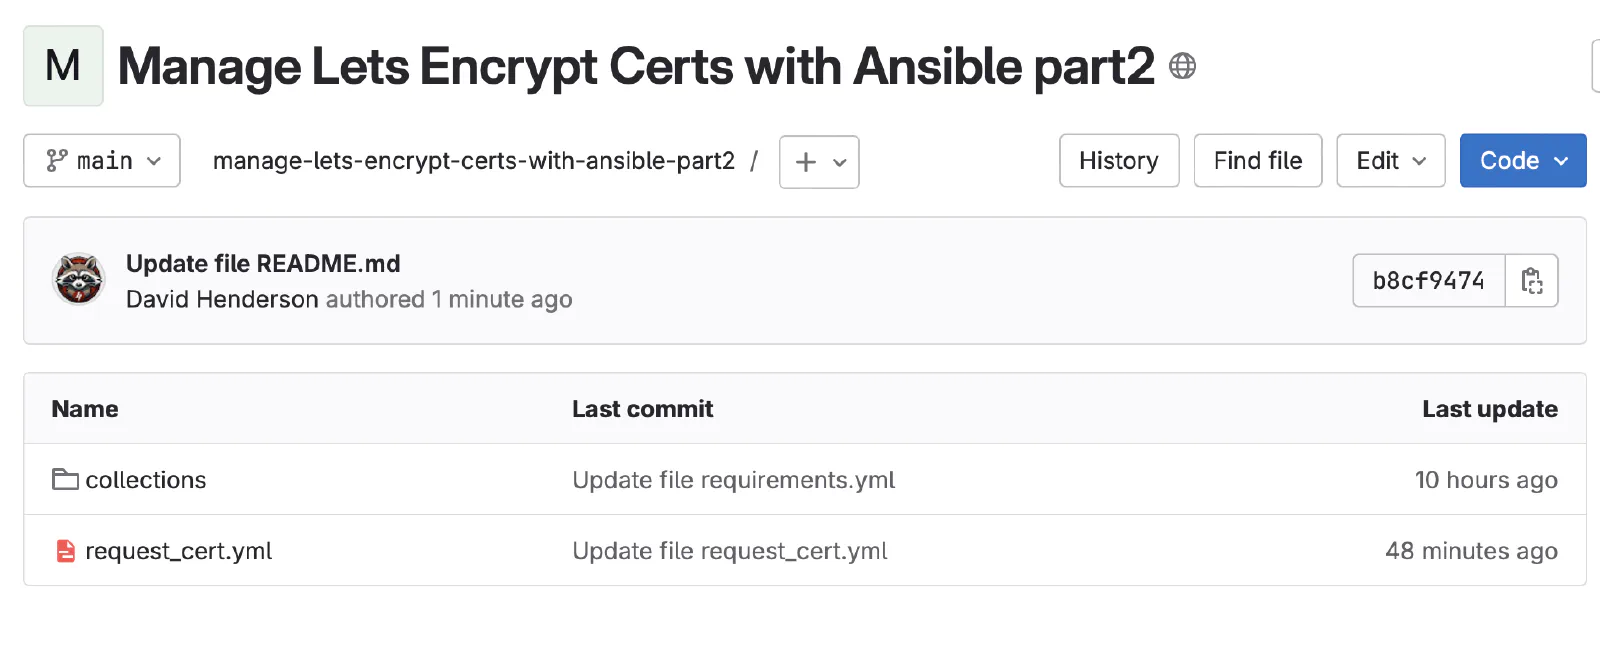
1.1. Copy or clone my repository for holding the playbook and other required files.
- request_cert.yml - main playbook
- Collections
- requirements.yml - AWX/AAP reads this file and installs dependant modules.
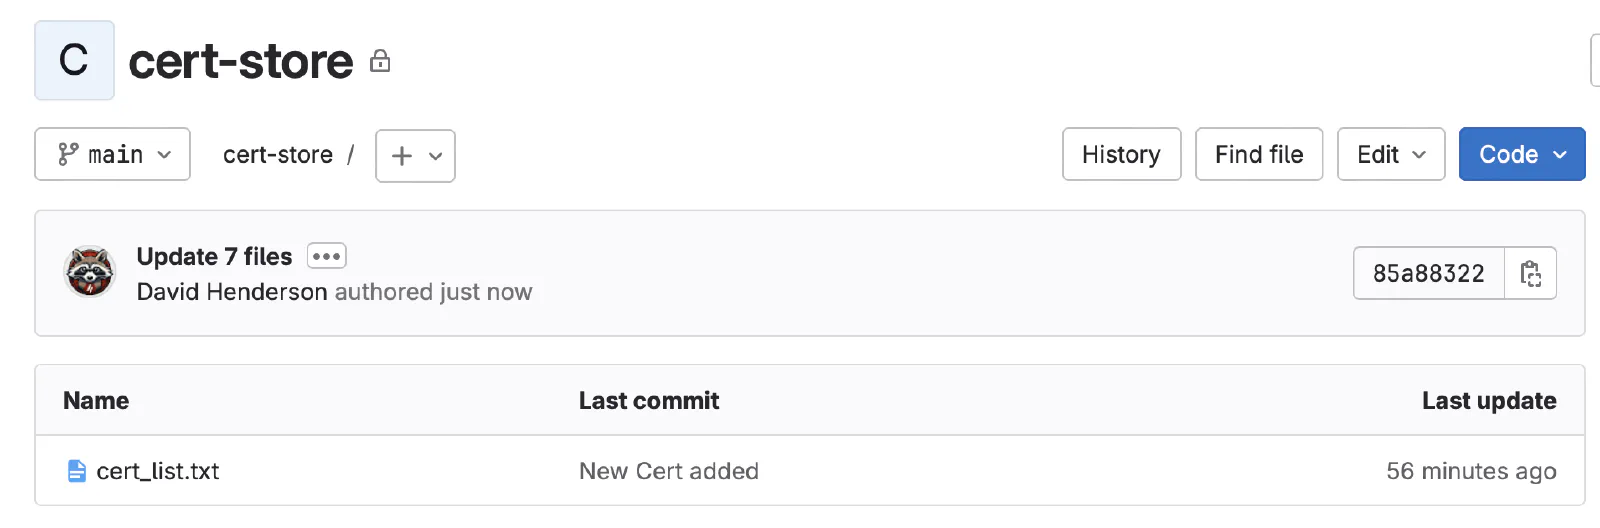
1.2 Create a new blank project in gitlab named cert-store
Create a empty file named cert_list.txt
Your repository should look like this
1. Ansible Setup Configuring AWX/AAP
1.1 Setting Up AWX
Ensure that AWX or Ansible Automation Platform is installed and accessible. Follow the official AWX installation guide if needed.
1.2 Creating custom credentials
AWX/AAP has built in templates for adding passwords and variables. but not all credentials fit into their templates. SO they give you the ability to create custom credentails.
We need to create a few Custom credentials:
- gitlab credentiails for our cert-store repository.
- Cloudflare API
Navigate to Administration go to the Credential Types section.
Add a New Credential Type: Click Add
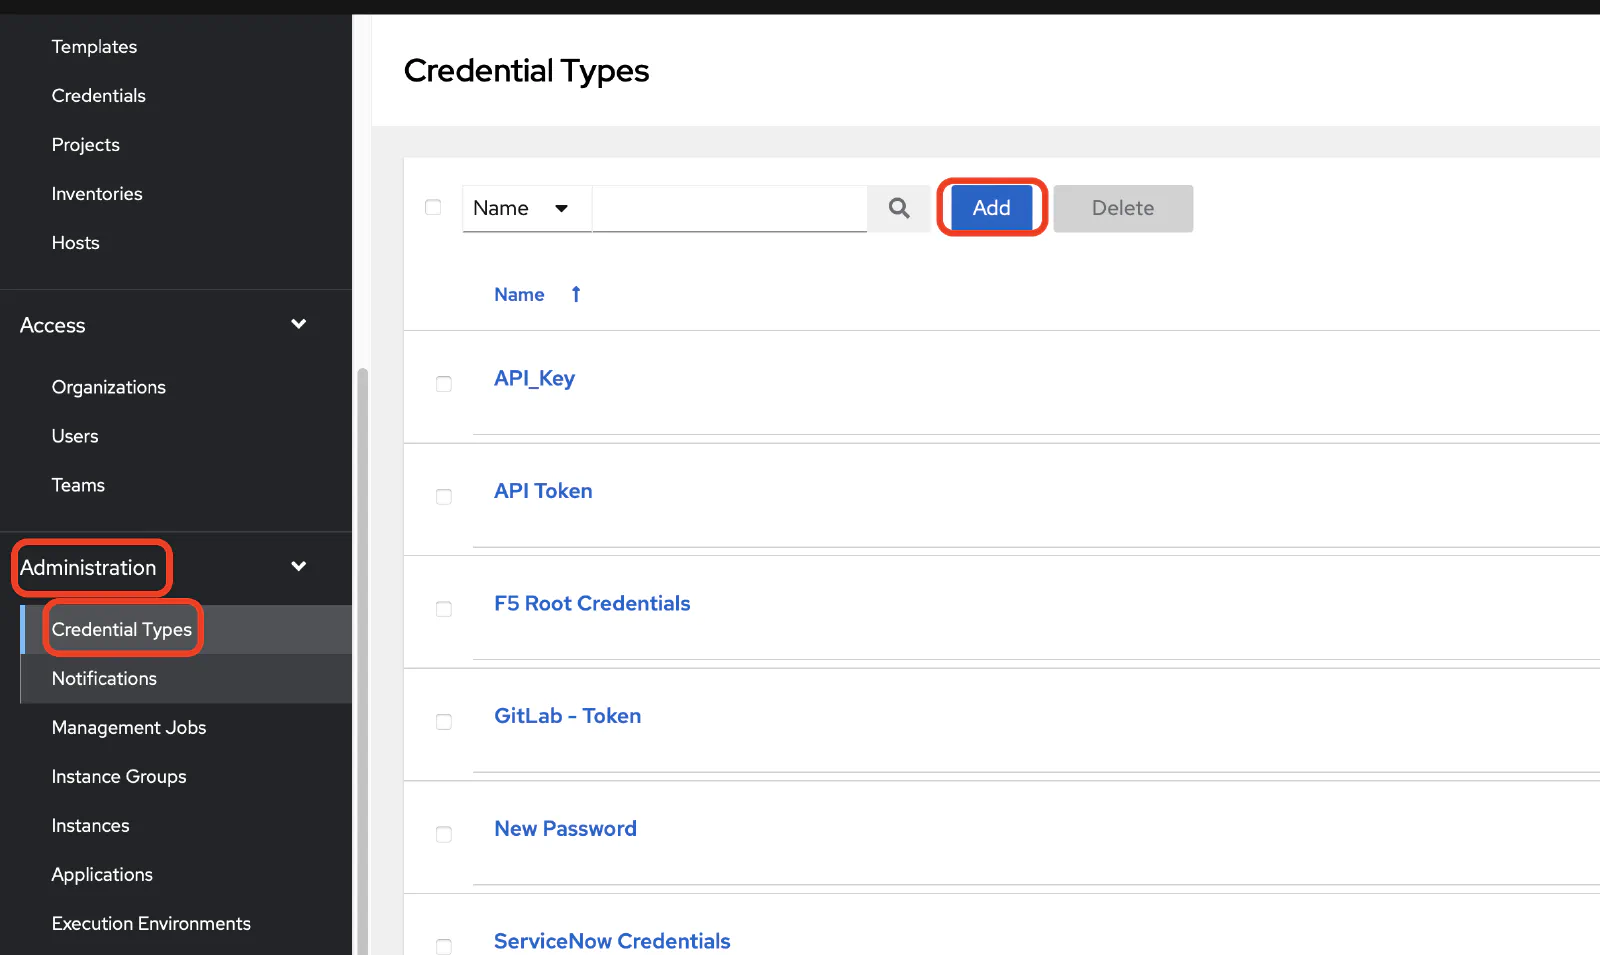 and fill in the following details:
- Name:
API_Key- Input Configuration:
--- fields: - id: api_key type: string label: API Key secret: true required: - api_key- Injector configuration:
---
extra_vars:
  API_key: '{{ api_key }}'
Add another New Credential Type: Click Add and fill in the following details:
- Name:
Gitlab Credentials- Input Configuration:
--- fields: - id: gitlab_username type: string label: GitLab username secret: false - id: gitlab_password type: string label: GitLab password secret: true - id: gitlab_project type: string label: GitLab project secret: false required: - gitlab_username - gitlab_password- Injector configuration:
---
extra_vars:
  gitlab_project: '{{ gitlab_project }}'
  gitlab_password: '{{ gitlab_password }}'
  gitlab_username: '{{ gitlab_username }}'
1.3 Creating New Credentials using our ne custom templates
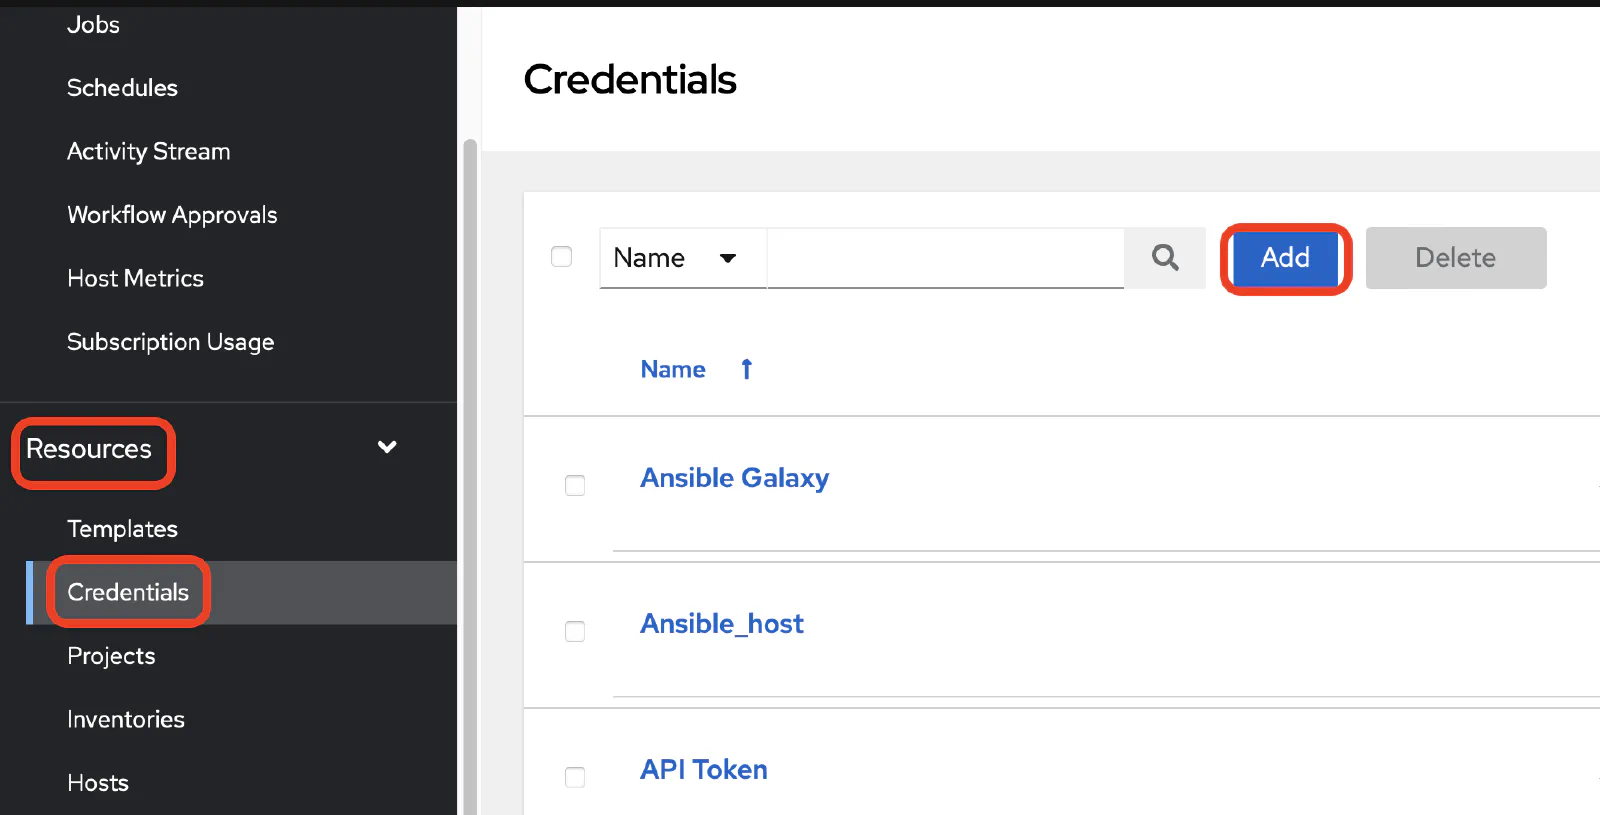
- Navigate to Resources go to the Credentials section.
- Add a New Credential: Click Add and fill in the following details:
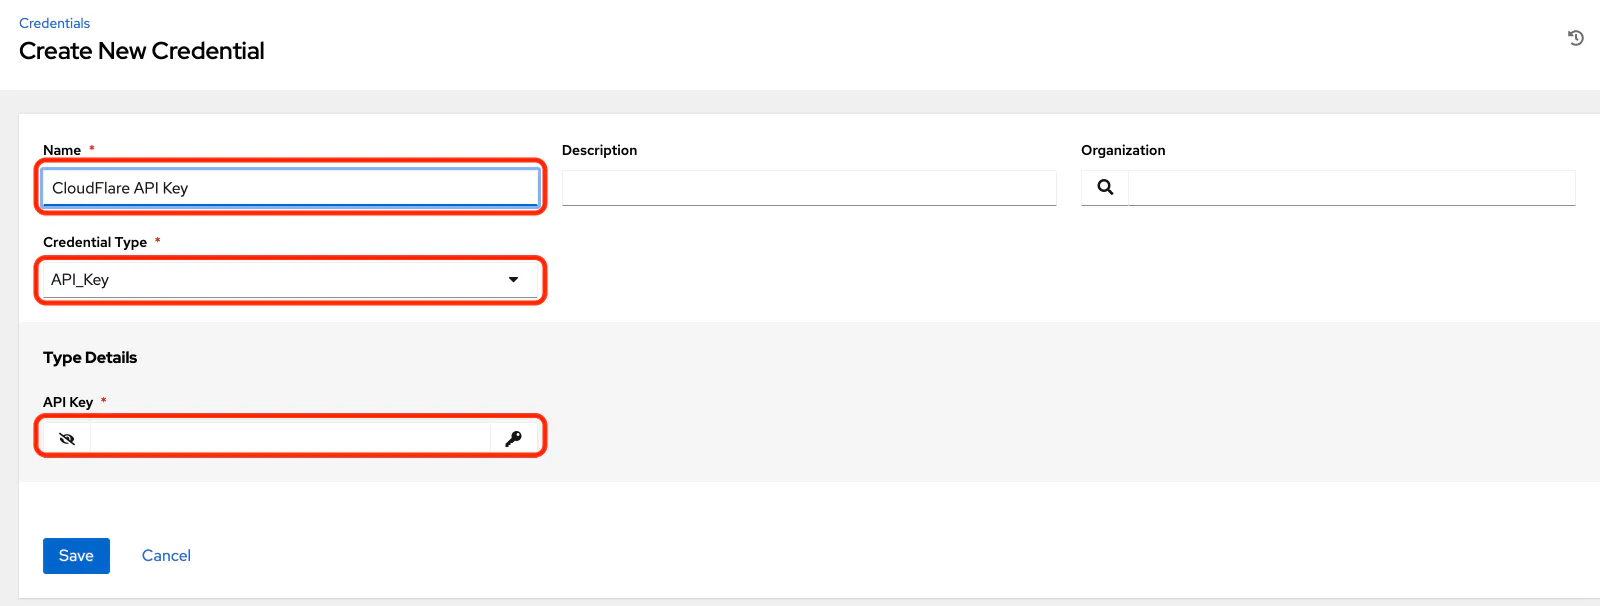
The first one we will create is the CloudFlare API token. use the template we created API_Key
- Name: CloudFlare API Key
- Organization: Your organization or default
- Credential Type: API_Key
- Type Details: Enter your GitLab credentials (username and password/token).
 Gitlab Credentials
- Add another custom credential: Click Add again
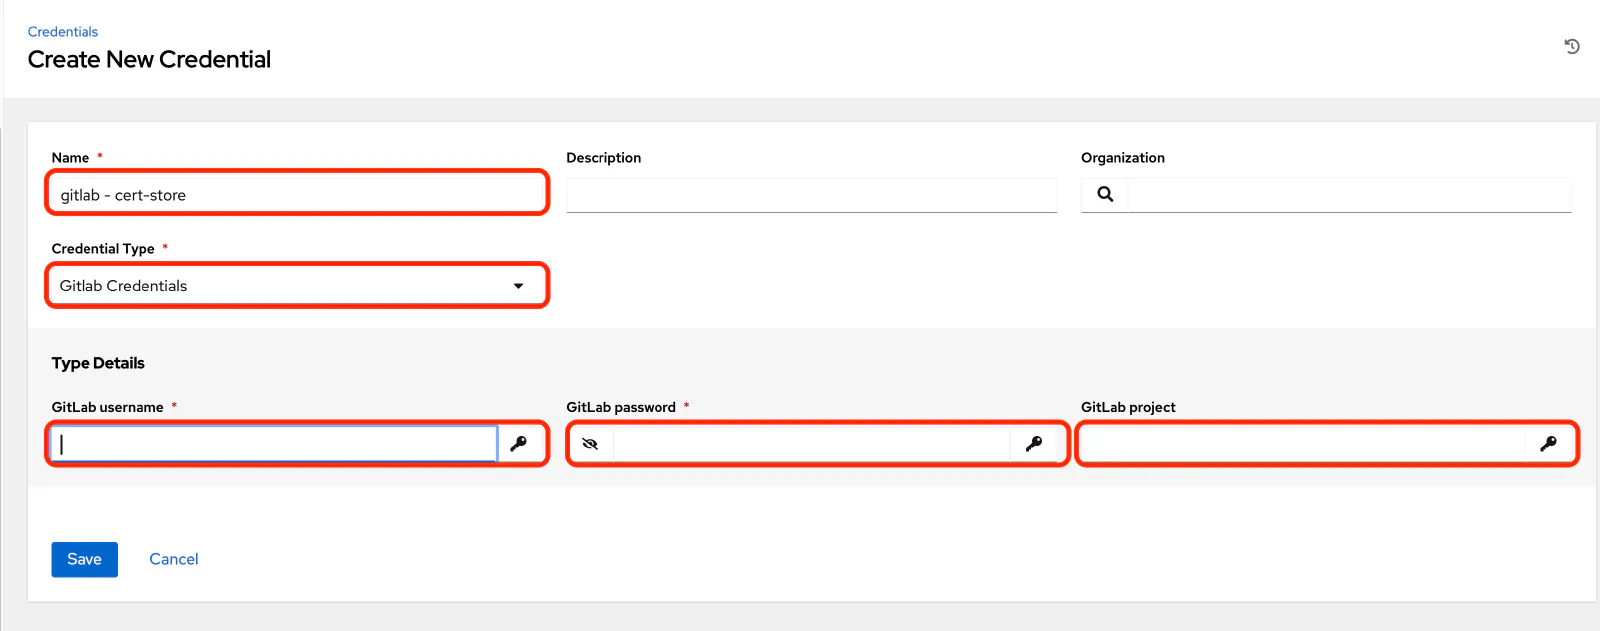
Next we will create credentials for Gitlab so we can clone and update teh cert-store repository. CloudFlare API token. use the template we created API_Key Fill in the following details:
- Name: gitLab - cert-store
- Organization: Your organization or default
- Credential Type: Gitlab Credentials
- Type Details: Enter your GitLab credentials for cert-store (username, password, project=cert-store).
- Add a New Source Control Credential:
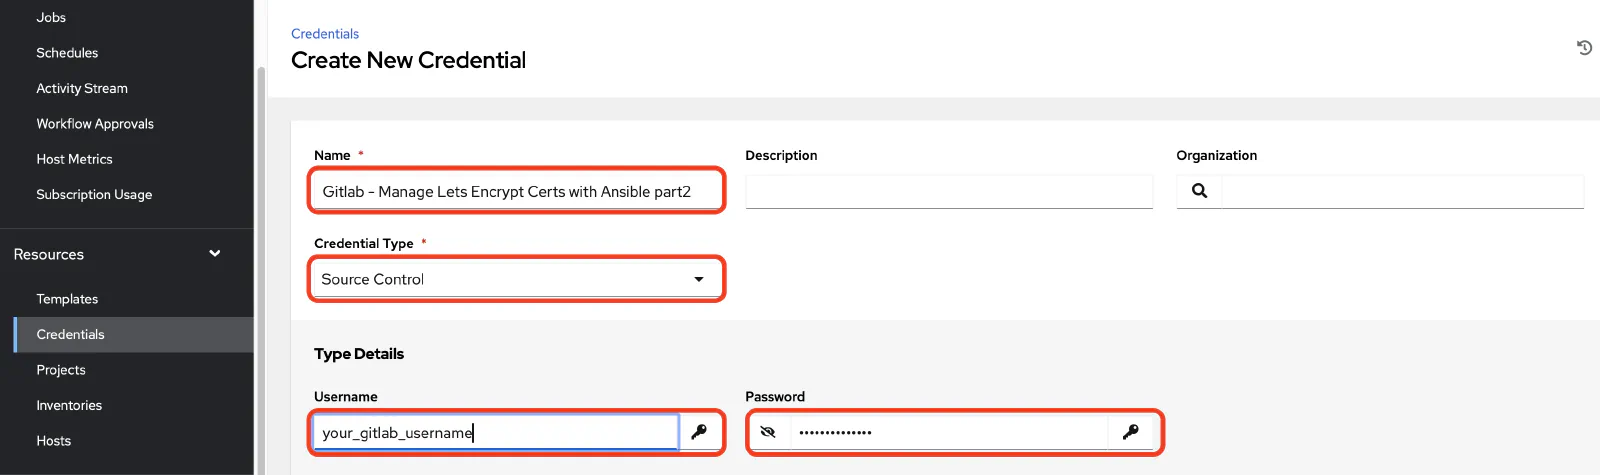
Now we will create credentials so we can run our playbook. We will need to create a source control credential for the Gitlab project that contains the playbook request_cert.yml
and fill in the following details:
- Name: gitLab Access
- Organization: Your organization or default
- Credential Type: Source Control
- Inputs: Enter your GitLab credentials (username and password/token).
1.4 Creating a New Project
Projects are how AWX/AAP sync the playbooks from your gitlab repository to the local execution evironment.
- Navigate to Resources go to the Projects section.
- Add a New Project: Click Add
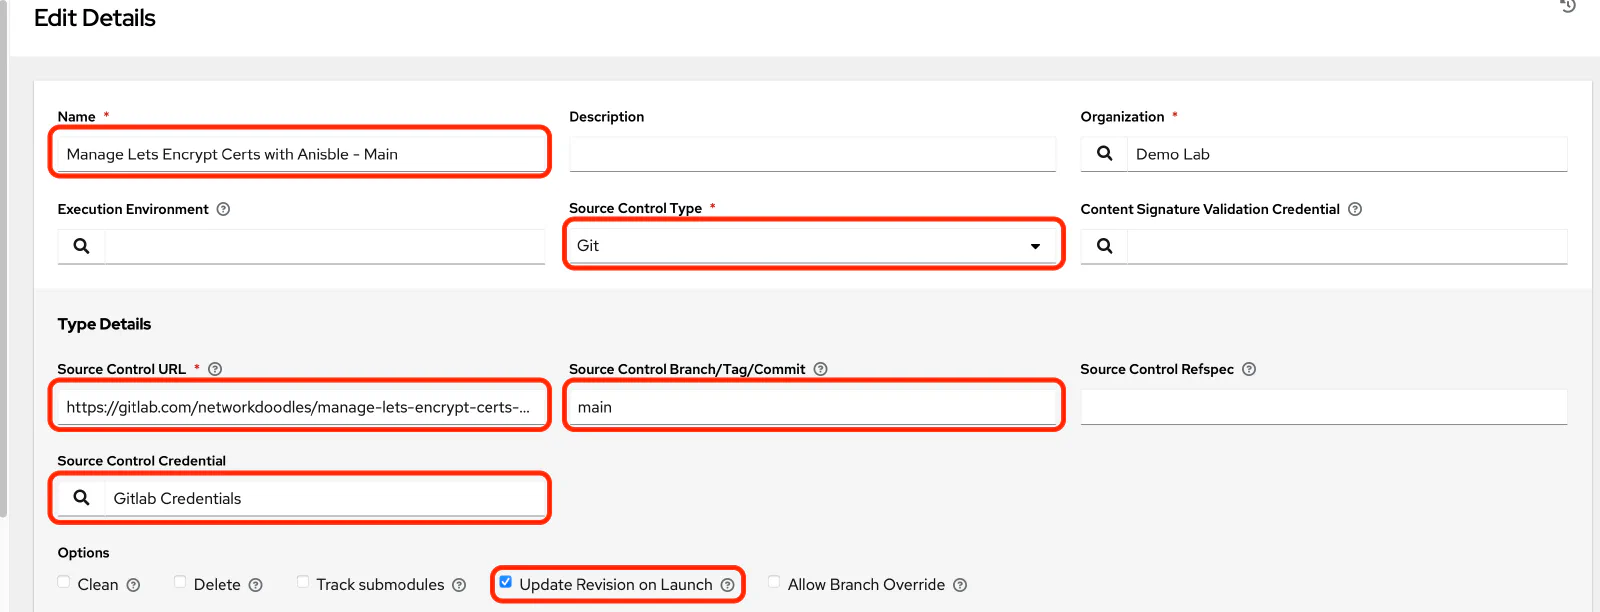
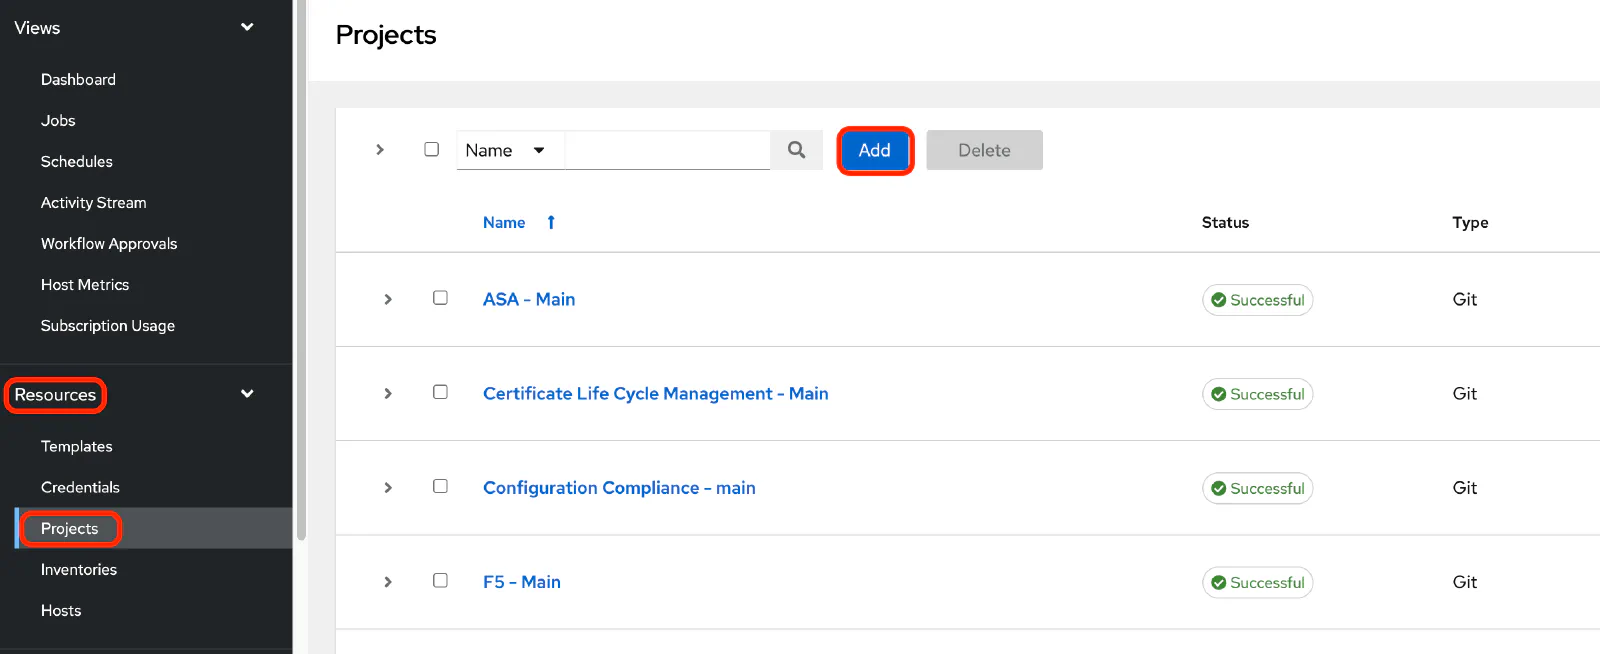 fill in the following details:
- Name: your_repo_name - main(branch)
- Organization: Your organization
- SCM Type: Git
- SCM URL:
https://gitlab.com/your-username/your-repo.git - SCM Branch/Tag/Commit: main
- SCM Update Options: Check Clean and Delete before update.
1.5 Creating a New Job Template
Templates are how AWX/AAP defines specific parameters, configurations and run playbooks
Navigate to Resources go to the Templates section.
Add a New Job Template: Click Add
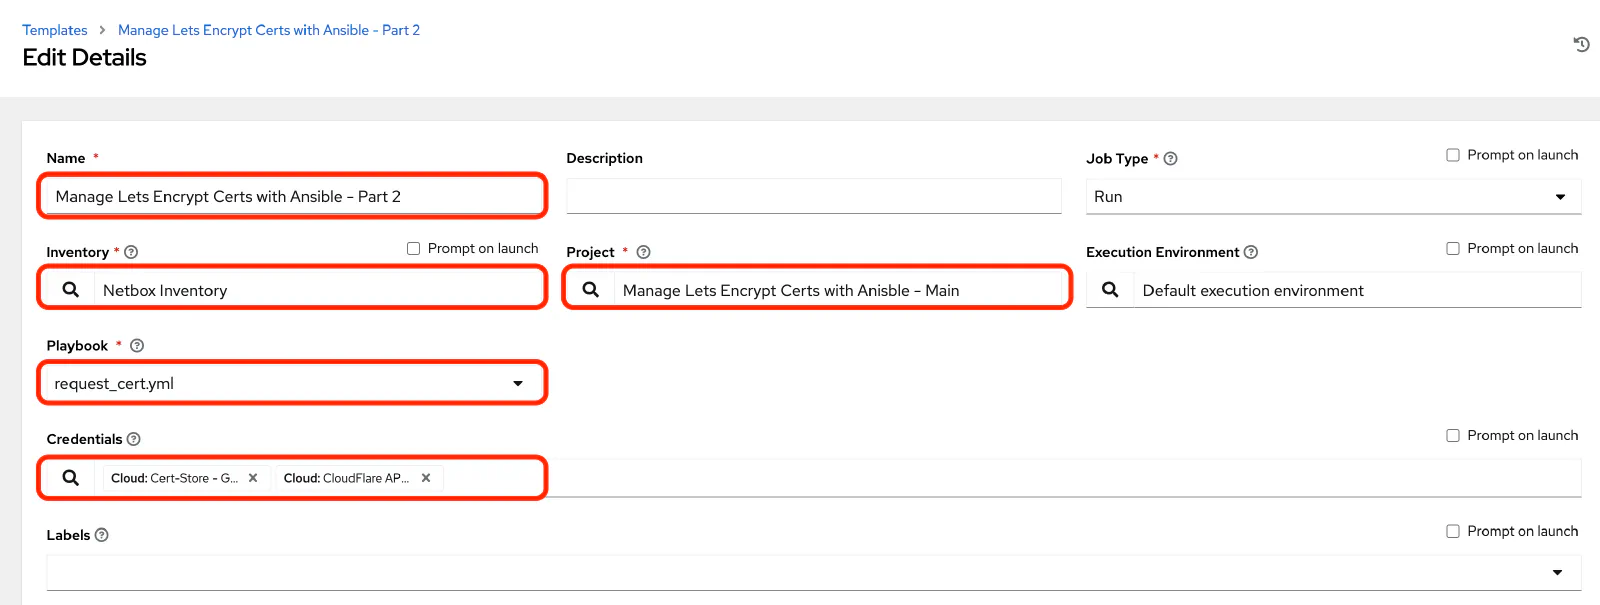
fill in the following details:
- Name: your_repo_name - playbook name
- Job Type: Run
- Inventory: Demo
- Project: project_created_in_last_step
- Playbook:
request_cert.yml - Credentials: Select the credentials for cert-store and cloudflare API.
1.6 Add a Survey to the template
Once the template is create we will add a survey to collect the certificate url and email variables.
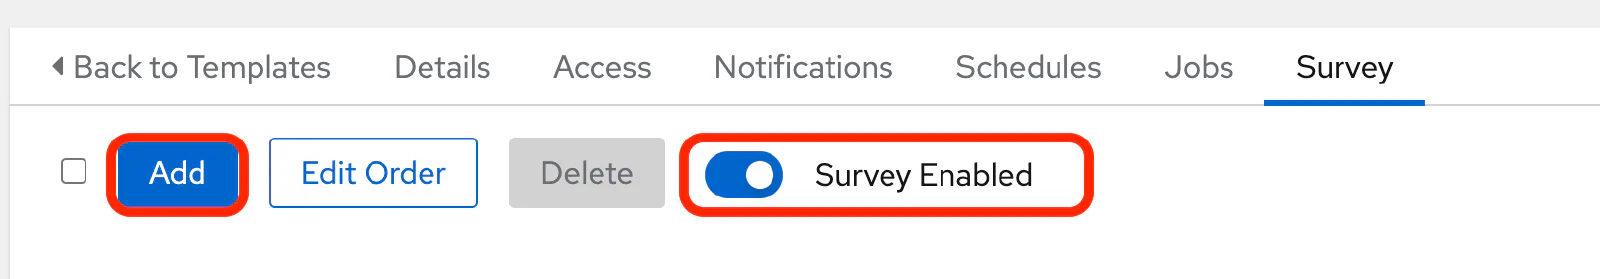
- After you saved your template you should have been teken to the details screen. from there click survey
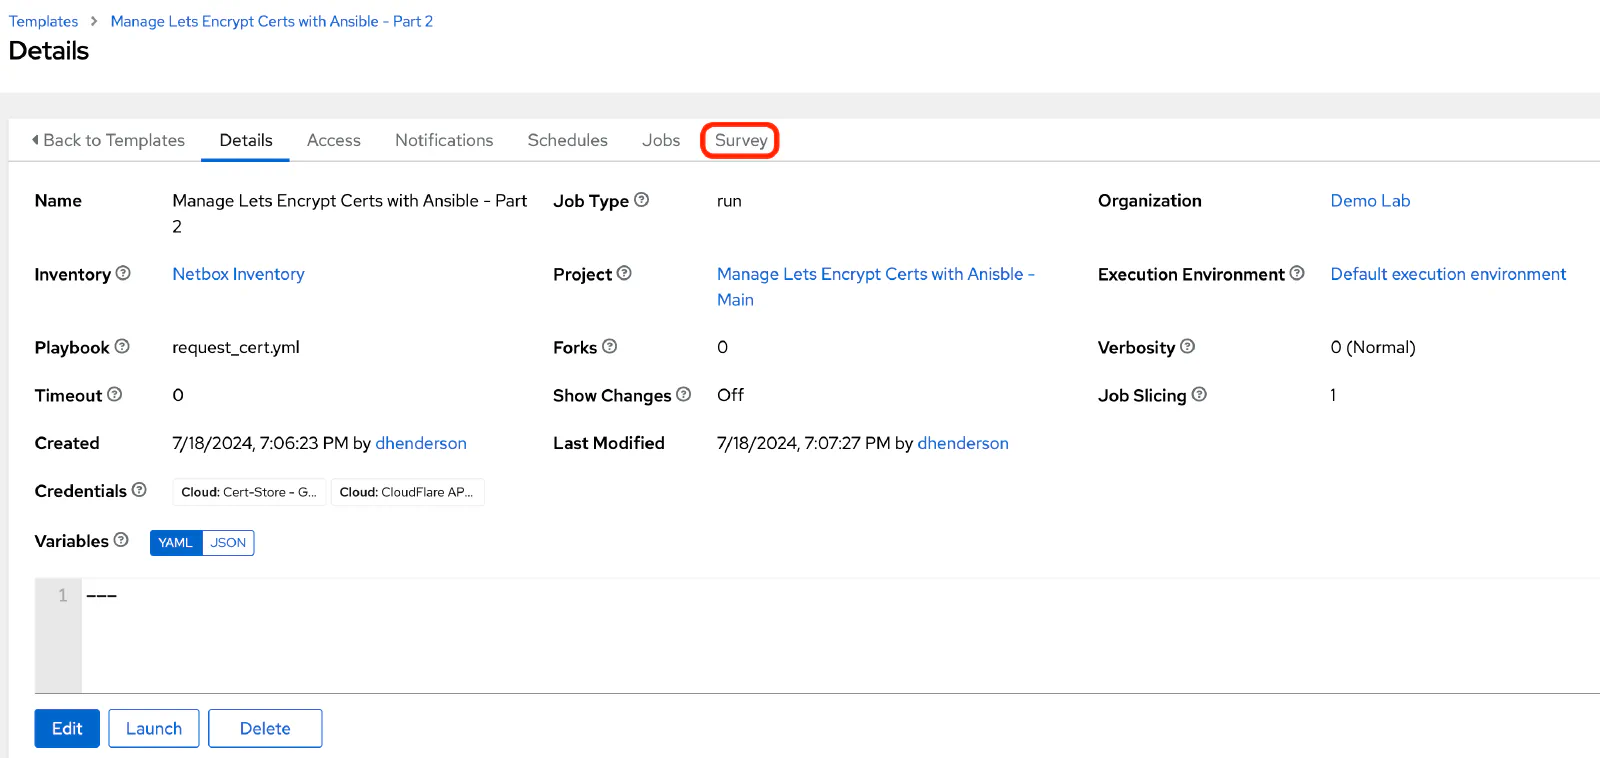
- enable the survey option and create two questions
- Question 1: Url for the cert
- Variable name:
fqdn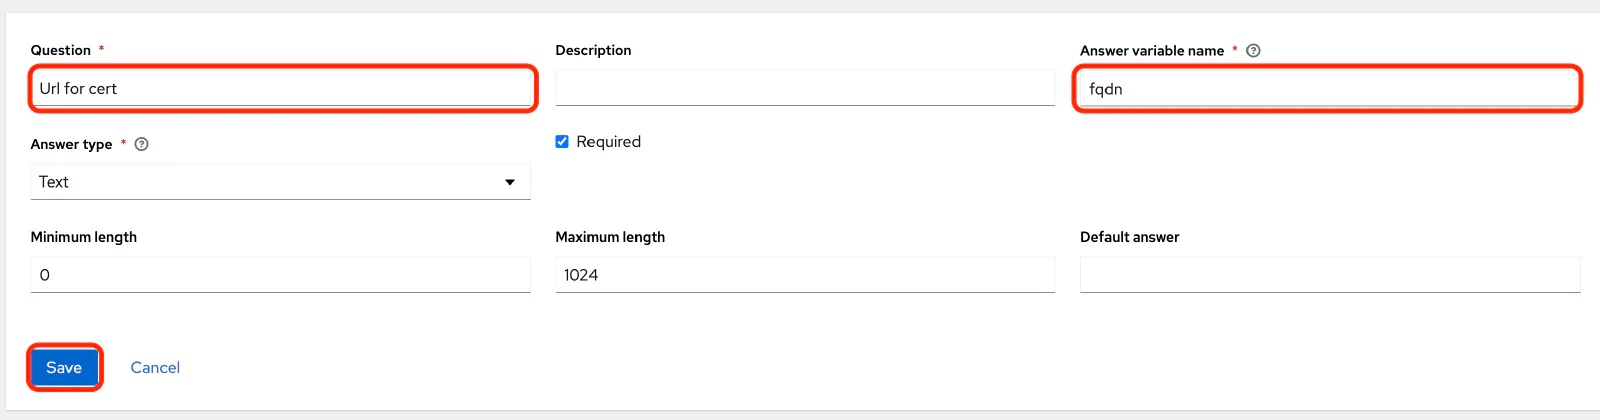
- Variable name:
- Question 2: Enter Email Address
- Variable name:
email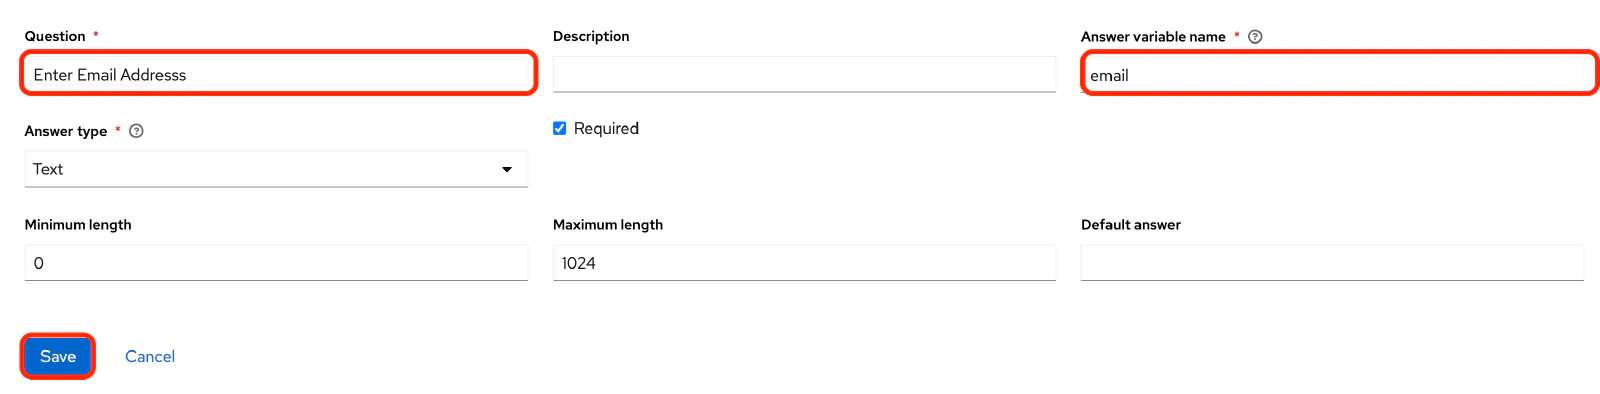
- Variable name:
- Question 1: Url for the cert
2. Running Playbooks
The playbook is run from the template we just created
Navigate to Resources go to the Templates section.
Click Rocket icon to the right of template we just created
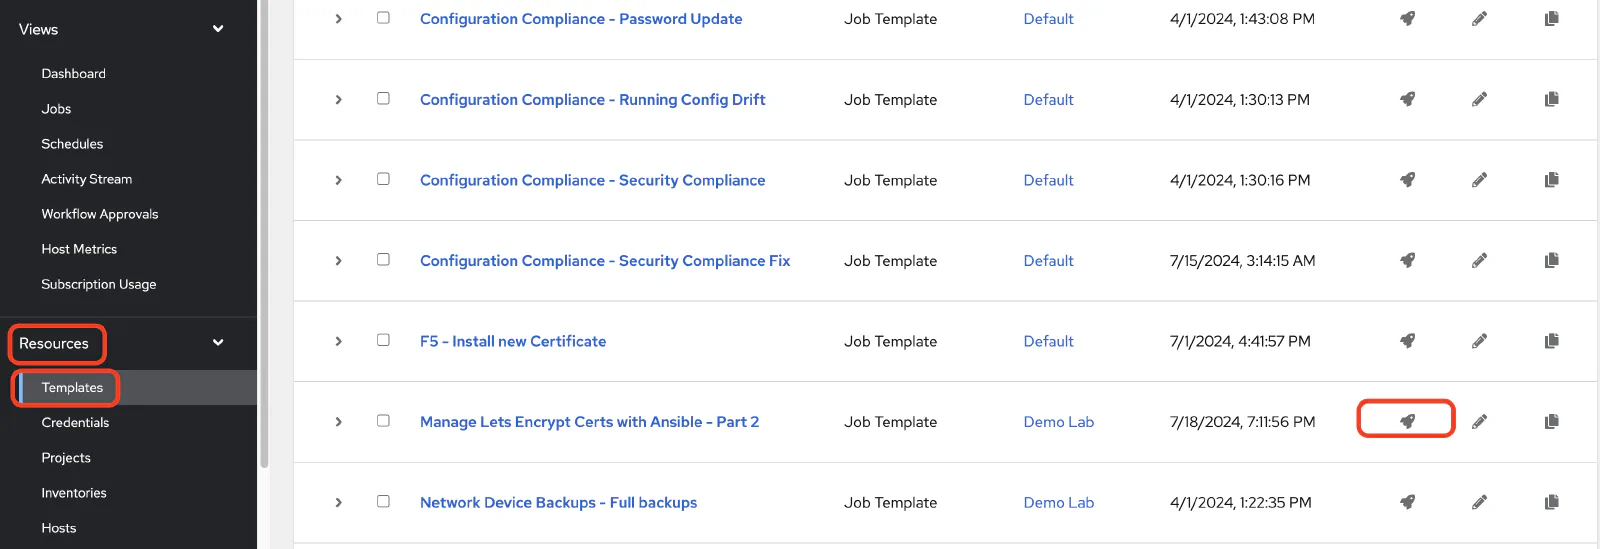
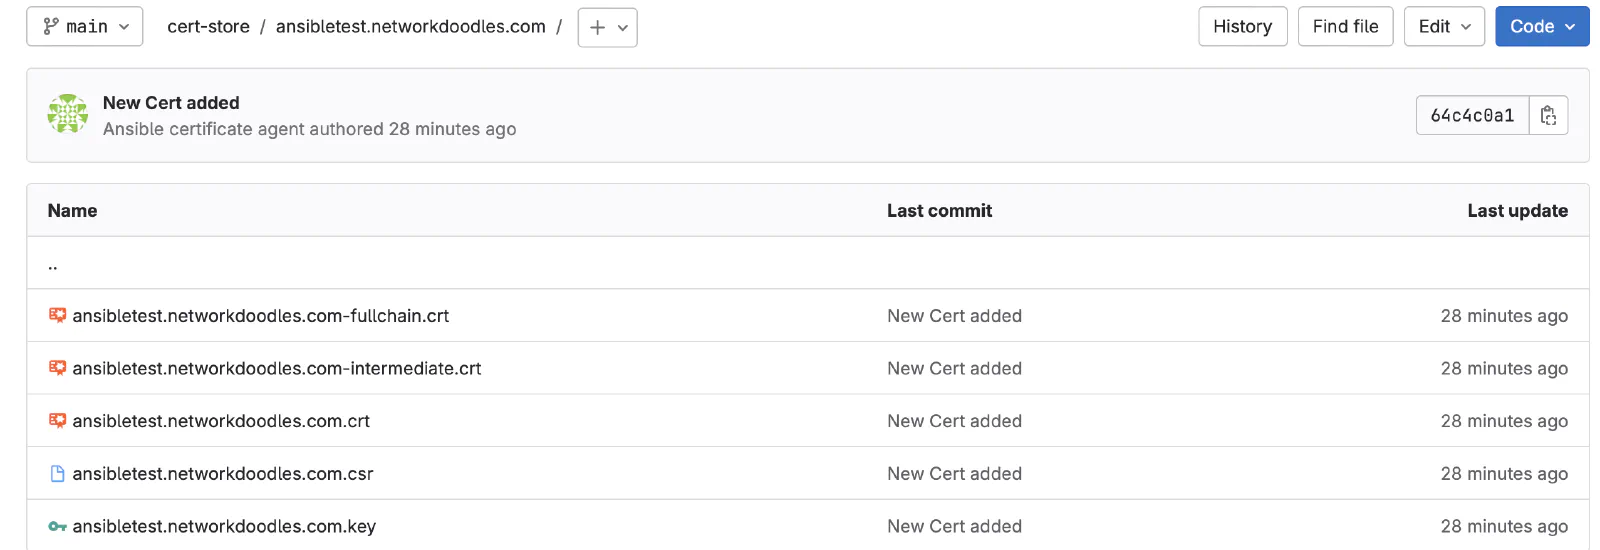
if sucessfull a sucess message will be displayed and your cert will be in your cert-store gitlab repository
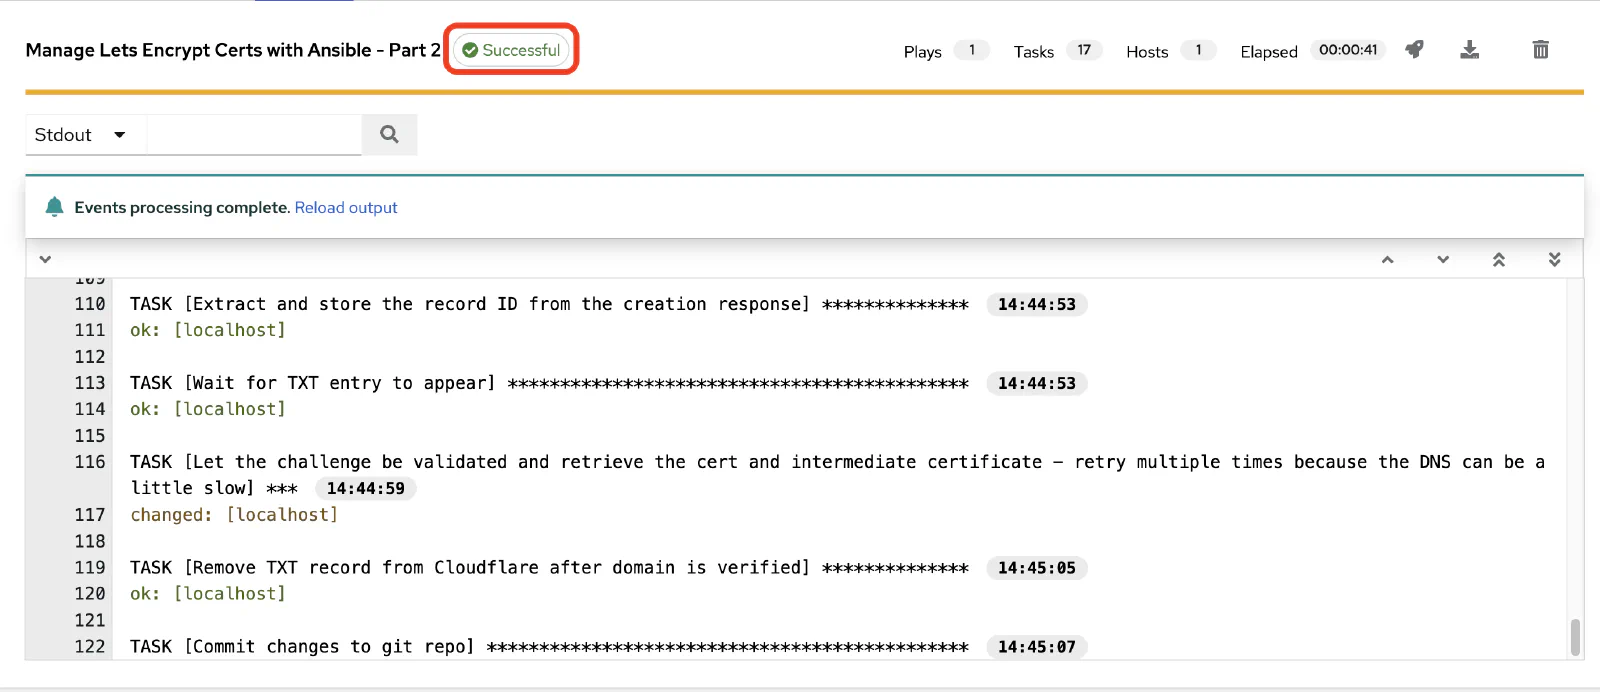
Verify in GitLab: Check your GitLab repository to ensure the certificates are updated.
Conclusion
In this part, you learned how to manage Let’s Encrypt certificates using AWX/Ansible Automation Platform integrated with GitLab for GitOps. This setup allows automated certificate requests, storage, and versioning.
Next Steps
This post is part of the Let’s Encrypt with Ansible series:
Related doodles
Managing TLS Certificates Using Ansible and Let’s Encrypt! PART 1:
This tutorial will guide you through the basics of using Ansible Core to request a Let's Encrypt certificate, securely storing your Cloudflare API …
How to Use NetBox as an Inventory in Ansible Core
How to Use NetBox as an Inventory in Ansible Core where I show you how into integrate NetBox Labs, with Ansible by Red Hat Core using a YAML …
Understanding YAML Files: A Guide for Network Engineers
Discover the power of YAML (YAML Ain't Markup Language) in network engineering a crucial tool for configuring and managing complex network …